
← Back to projects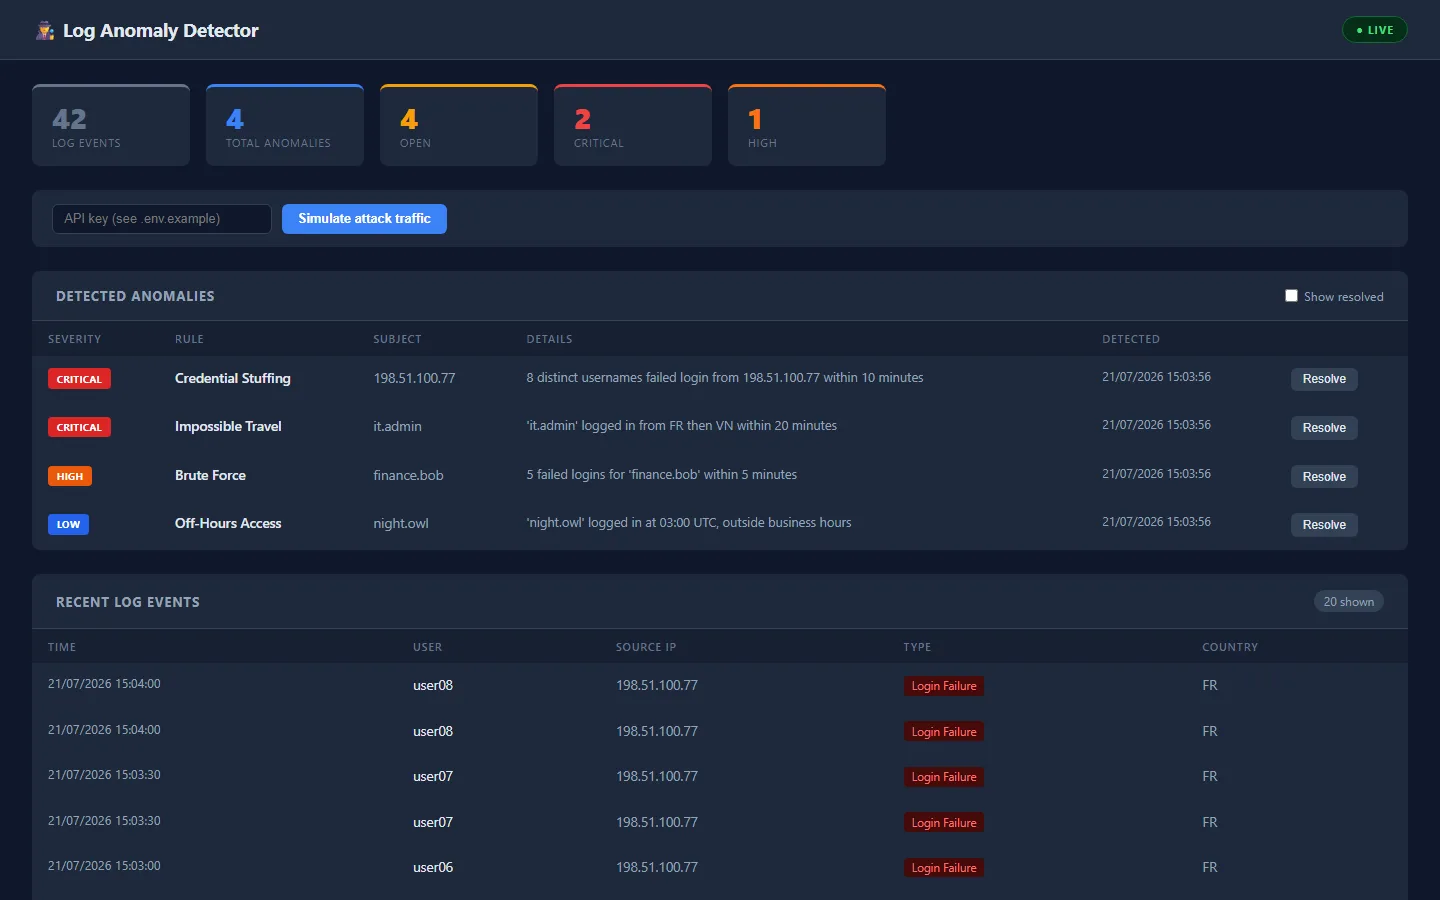
Personal project
Log Anomaly Detector — Rule-Based Auth Log Analysis
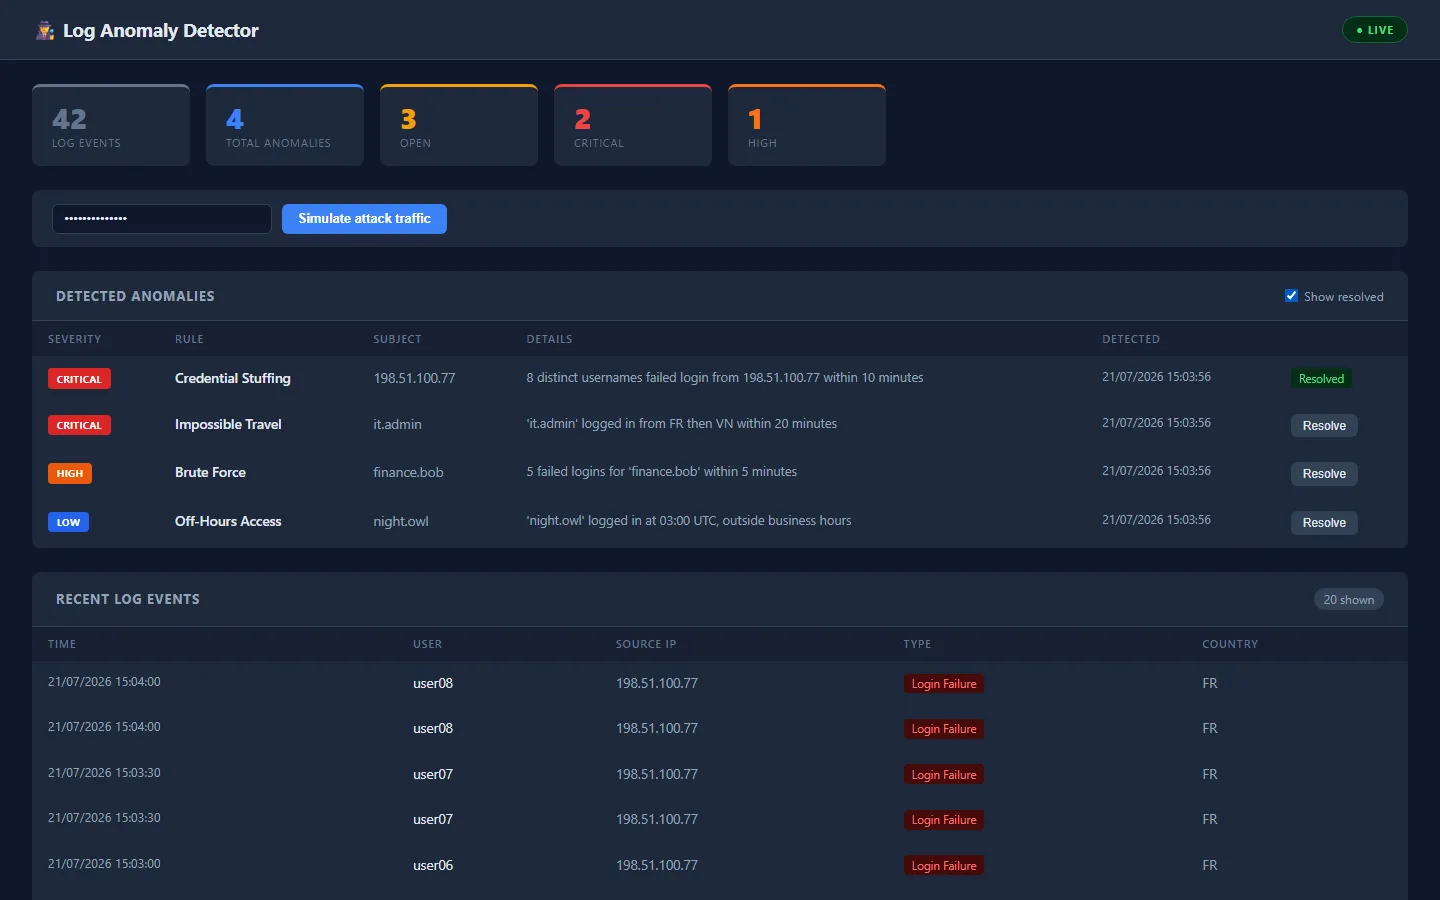
Rule-based detection engine for authentication logs, surfacing brute-force attempts, impossible-travel logins, credential-stuffing bursts, and off-hours access — each rule a pure, unit-tested function with zero I/O.
Context
Most SOC dashboard demos display alerts that already exist somewhere else. This one generates them — reasoning over sequences of events instead of filtering pre-labeled data.
What I built
- I wrote four independent detection rules (detection.py) as pure functions: brute force, impossible travel, credential stuffing, off-hours access
- I built a windowing + dedup layer so a sustained attack does not spam duplicate anomalies
- I designed a deterministic demo scenario, anchored to a fixed time-of-day so tests never depend on real wall-clock time
- I added a Simulate attack traffic button replaying that scenario live from the dashboard
- I wrote 20 Pytest tests — all 4 rules unit-tested with plain event dicts, zero database or clock dependency
Verified live
1
Anomalies per rule
Each rule fires exactly once per scenario run
0 new
Dedup on replay
Re-running the scenario correctly creates zero duplicates
4
Detection rules
Brute force, impossible travel, credential stuffing, off-hours
Screenshots