
← Back to projects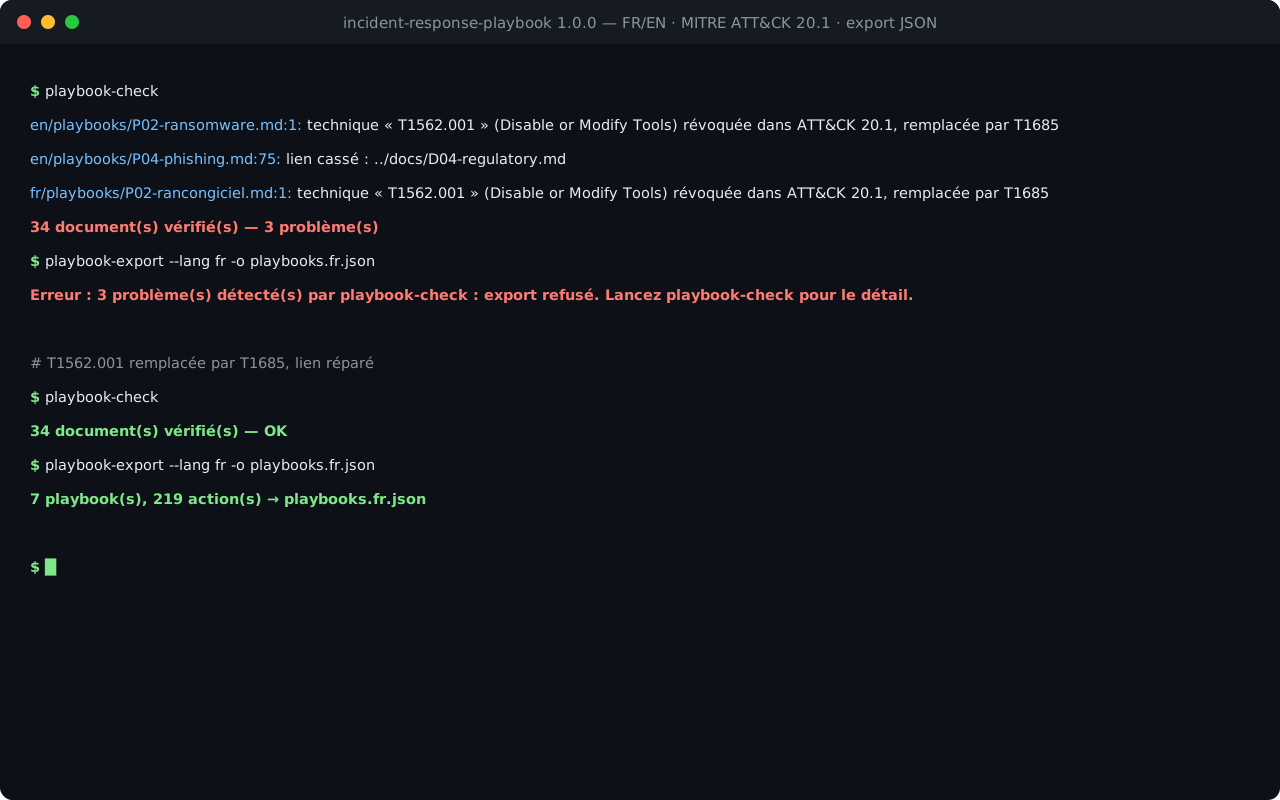
Personal project
Incident Response Playbook — bilingual SOC procedures
Seven incident response playbooks a team can follow under pressure, in French and English — with legal deadlines, evidence handling and MITRE ATT&CK mapping, all checked automatically in CI
Context
I rebuilt this project from scratch by merging my two older repositories (one English, one French) into a single bilingual reference. The aim is practical: when an incident starts, a SOC analyst or an IT admin in a small or mid-sized company should know who does what, in which order, which evidence to keep and which deadlines apply — without having to interpret a framework. The procedures follow NIST SP 800-61 Rev. 3 (April 2025, aligned with CSF 2.0) and map every attacker behaviour to MITRE ATT&CK.
What the repository contains
- 7 playbooks: malware, ransomware, data breach, phishing, unauthorised access, denial of service, and compromised account with payment fraud
- The same 8 numbered phases in each: detection, triage, containment, evidence, eradication, recovery, obligations and communication, closure — with checklist actions
- 6 reference documents: severity levels S1–S4 and timelines, escalation, RACI matrix, regulatory context, evidence preservation, and a ransomware tabletop exercise
- 4 templates: incident report, blameless post-mortem, crisis communication (staff, customers, GDPR article 34, press) and evidence log with chain of custody
- Everything in French and English, with the same metadata in both languages
Legal and evidence choices
- GDPR articles 33 and 34: notification to the CNIL within 72 hours and information of the people affected when the risk is high
- NIS 2 article 23: early warning within 24 hours, notification within 72 hours, final report within one month — the French transposition flagged as still in progress
- French Insurance Code article L. 12-10-1: police complaint within 72 hours to be compensated for a cyberattack
- Evidence collected in order of volatility (RFC 3227), SHA-256 hashes and a chain of custody; machines isolated, never switched off
- Public contacts verified on official sources: 17Cyber, Cybermalveillance.gouv.fr, CERT-FR, CNIL, Signal Spam and 33700
Automated checks
- Every document starts with a structured front matter (strict YAML subset) rendered as a table on GitHub
- playbook-check verifies required fields, FR/EN parity of severities and techniques, the 8-phase structure with actions to tick, and every internal link
- Each MITRE ATT&CK technique is checked against the official 20.1 data bundled with the tool: unknown or revoked techniques are rejected with their replacement, and each one must be explained in the text
- playbook-export turns the documentation into JSON — checklists, severity grid and legal deadlines read from the Markdown tables — and refuses to export anything if a single problem remains
Web interface
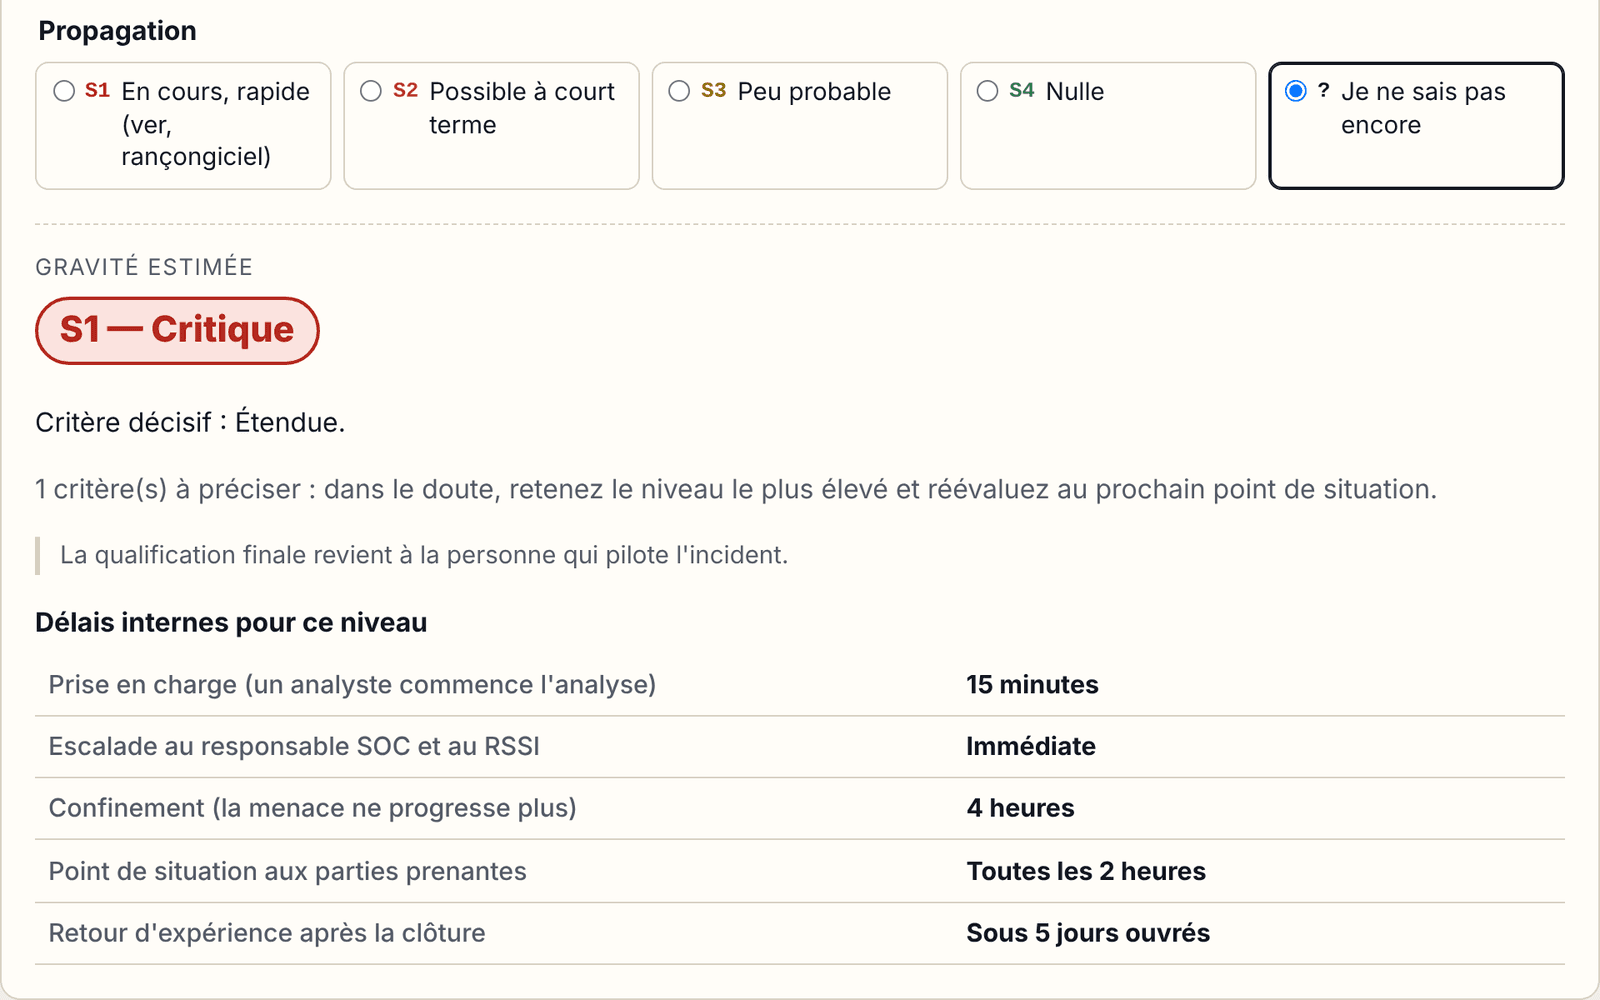
- Severity triage on the five criteria of the severity grid: the most severe wins, a playbook can raise the level but never lower it
- Playbook choice from each playbook's "when to use it" paragraph
- Legal deadline countdowns from the time the incident became known: GDPR 72 h, NIS 2 24 h and 72 h, police complaint 72 h
- Timestamped checklist of the 8 phases and a Markdown report in UTC, ready for the incident report
- Strict content security policy, no analytics or cookies, nothing kept by default; published on GitHub Pages from the same commit as the playbooks
Engineering quality
219
Checklist actions
per language, across 7 playbooks
142
Automated tests
108 Python (validator, export) + 34 web
7
CI jobs
Windows + Linux, Python 3.11/3.14, Ruff, documentation, web interface
0
Runtime dependencies
How it is used
- 1QualifyThe severity grid (S1 to S4) and the decision table point to the right playbook and the right people to notify.
- 2RespondThe team follows the 8 phases and ticks each action, preserving evidence before anything is cleaned.
- 3ReportLegal deadlines are tracked from the moment of awareness; templates cover the report, the communication and the evidence log.
- 4ImproveA blameless post-mortem and a yearly tabletop exercise feed the next version of the playbooks.
Screenshots