
← Back to projects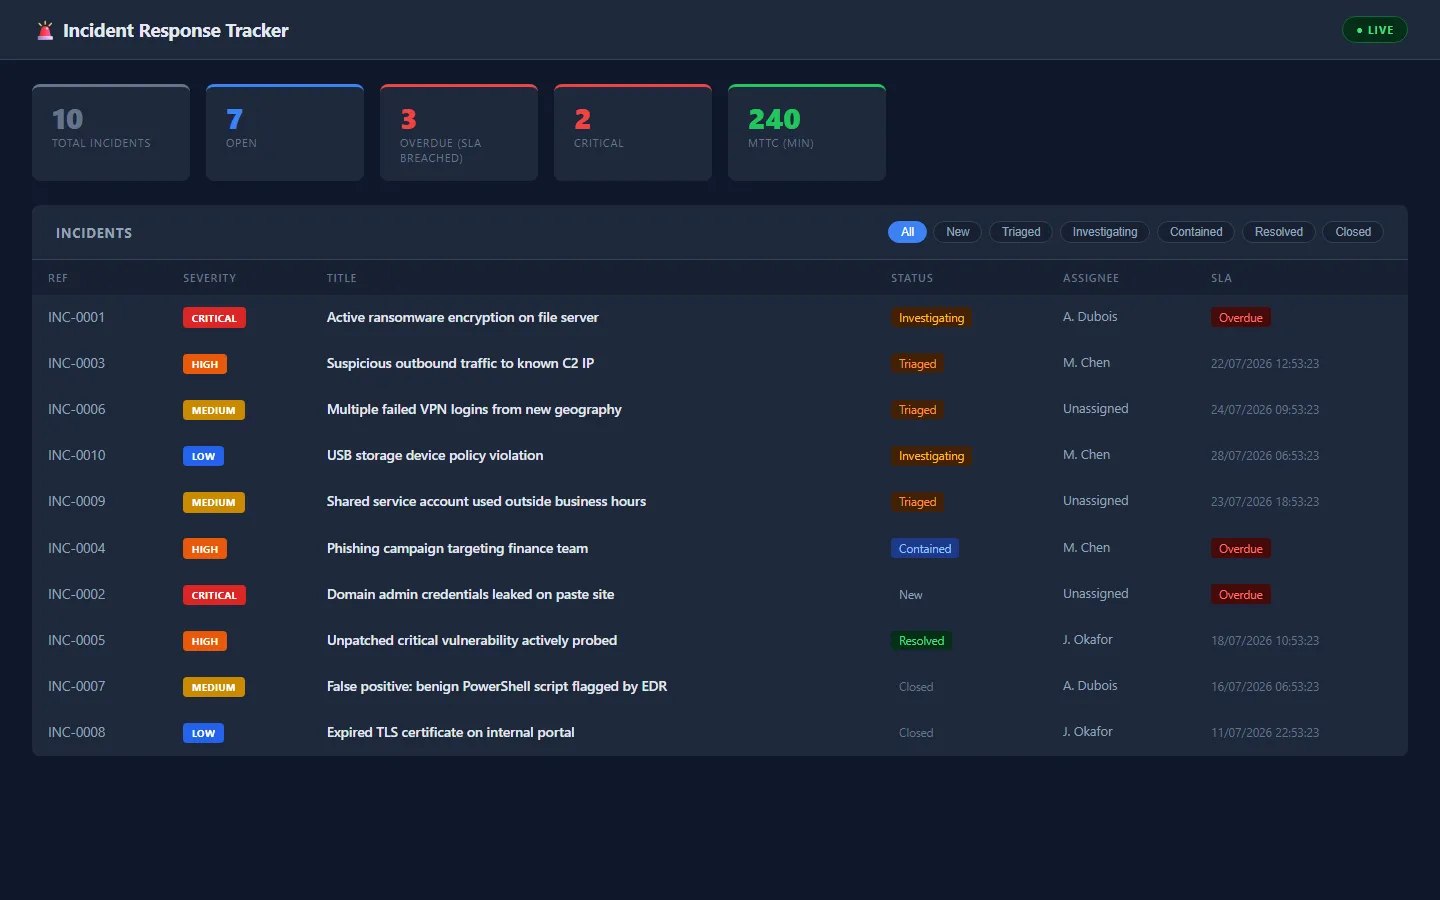
Personal project
Incident Response Tracker — SOC Ticketing Workflow
Ticketing workflow for security incidents enforcing a strict lifecycle via a state machine, a per-severity SLA clock, and a timestamped audit trail of every status change, comment, and assignment.
Context
A dashboard of alerts is only half the job — someone has to own each one until it is resolved, and prove the SLA was followed. This tracker enforces that workflow instead of leaving it to convention.
What I built
- I built a pure state_machine module defining every legal transition and per-severity SLA target, with zero I/O
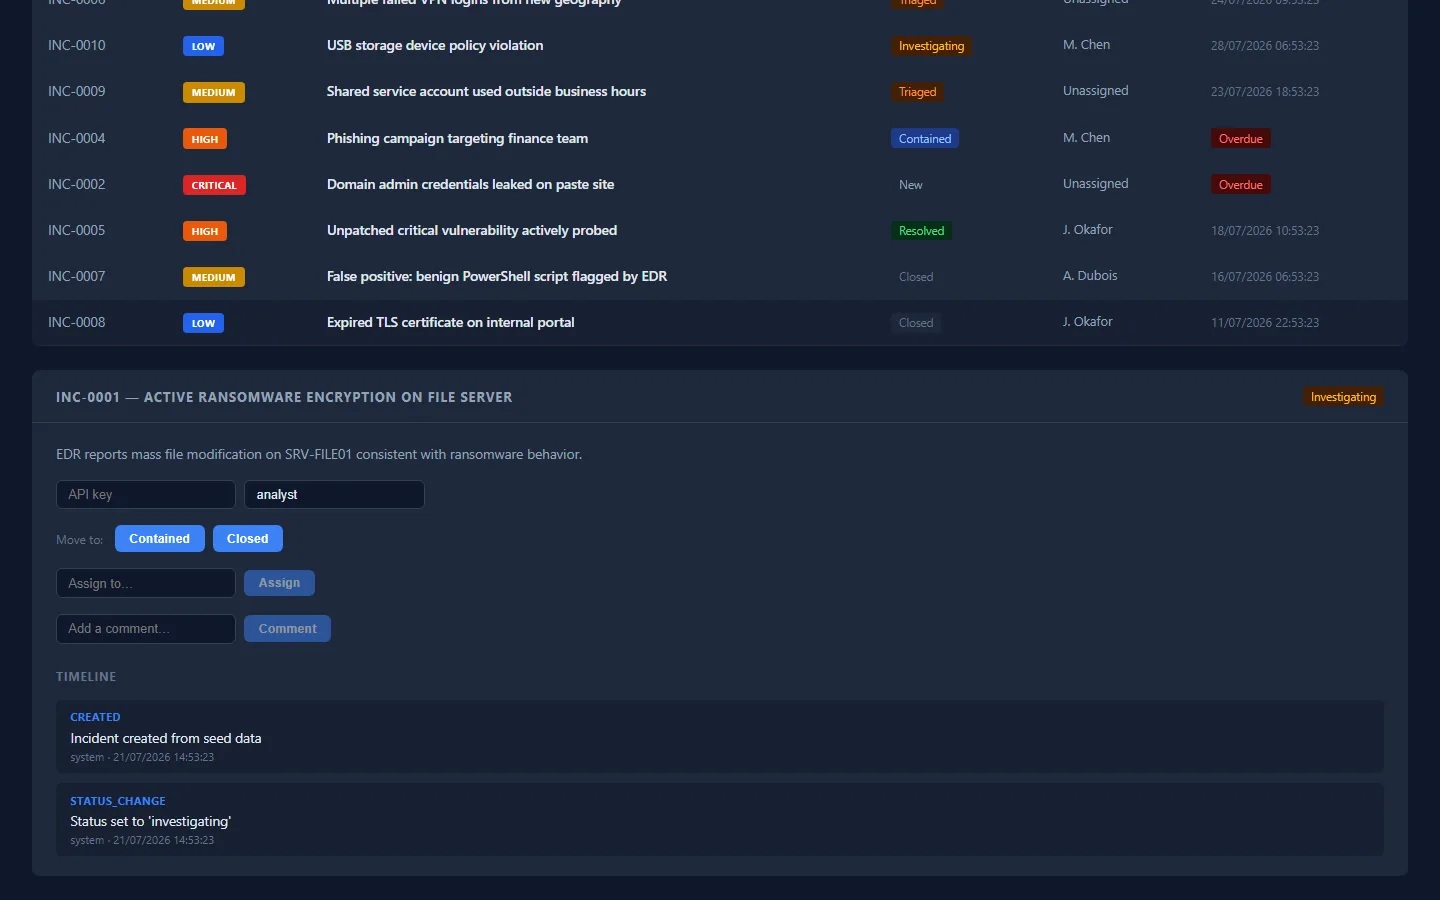
- I added FastAPI endpoints that reject illegal transitions with a 409 and the list of allowed next states
- I implemented a timestamped audit timeline — every status change, comment, and assignment recorded
- I built a React master-detail dashboard with inline status transition buttons
- I wrote 15 Pytest tests, including pure unit tests of the state machine independent of the database
Verified live
Rejected
Illegal transition test
new to resolved correctly returned HTTP 409
4
SLA tiers
Critical 4h / High 24h / Medium 72h / Low 7d
10
Seeded incidents
Spanning every lifecycle state
Screenshots